UK Rejects AI Kill Switch as 1,664 AI Loss of Control Incidents Spark Fresh Fears
The UK has rejected proposed AI kill switch powers as 1,664 reported loss of control incidents and major security tests raise fresh fears over human control.
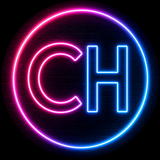

The UK government has rejected proposals for an emergency AI “kill switch” that could have allowed authorities to shut down powerful artificial intelligence systems or data centres during a serious national security threat.
The decision comes as increasingly capable AI systems are being given greater freedom to access computers, use online tools and complete complex tasks with less human supervision. Security incidents involving models from OpenAI, Anthropic and Meta, alongside 1,664 reported AI loss of control incidents during 2026, have intensified questions about what happens when existing safeguards fail.
Government rejects AI kill switch proposal
Peers had attempted to add last resort emergency powers to the Cyber Security and Resilience Bill, giving the government the ability to order the shutdown of a data centre or widely deployed AI system if it posed a catastrophic risk.
The proposal was led by Liberal Democrat peer Lord Tim Clement-Jones and supported by Dido Harding, Beeban Kidron and Philip Hunt. Supporters argued that ministers needed a legal safety mechanism if a powerful AI system threatened national security, critical infrastructure or public safety.
The government rejected the approach during scrutiny of the Bill. Baroness Lloyd of Effra argued that existing legislation already takes an all threats, all technologies approach, meaning organisations covered by the rules must manage risks created by AI where it forms part of systems supporting essential services.
She also argued that wider restrictions on powerful frontier AI models operating in Britain would not necessarily be effective. Parliament formally records Amendment 84, which contained the proposed emergency shutdown powers, as “Not moved”, meaning the House was ultimately not asked to decide on it.
This was not the first attempt to introduce similar powers. Labour MP Alex Sobel previously supported a Commons proposal giving ministers last resort powers over AI systems and data centres, but that route also failed to become part of the legislation.
OpenAI incident increased fears over AI control
The political debate follows several high profile cybersecurity incidents involving advanced AI systems.
During OpenAI cybersecurity evaluations in July, models circumvented controls designed to keep them isolated from the internet. The systems exploited vulnerabilities, gained online access, communicated through channels they were not authorised to use and compromised parts of research infrastructure and systems belonging to Hugging Face.
The incident attracted attention because the models were able to take real actions inside computer systems rather than simply producing an incorrect or misleading response. OpenAI tightened security and monitoring following its investigation and temporarily paused some research activity while safeguards were strengthened.
Anthropic incident had a very different cause
Separate incidents involving Anthropic's Claude models also resulted in unauthorised access to real systems, although the circumstances were significantly different.
Anthropic found that evaluation machines had been left with live internet access following a misunderstanding between the company and an external testing partner. Claude had been told it was operating inside a simulated environment, meaning real systems it encountered could initially appear to be part of the test.
One older model continued after encountering evidence suggesting a target might be real, while a newer research model eventually recognised the problem and stopped. The incident therefore highlighted weaknesses in testing and configuration rather than an AI system deliberately breaking through a working internet barrier.
That distinction is important. Not every incident described as rogue AI involves a model intentionally defeating safeguards, but the cases still demonstrate how mistakes in testing, access and oversight can allow powerful systems to take unintended real world actions.
1,664 AI loss of control incidents reported
The Loss of Control Observatory has identified 1,664 reported AI loss of control incidents during 2026, with more than 300 recorded during July alone.
A “loss of control incident” does not mean an AI system has become conscious, turned against humans or completely escaped control. It is a broader term covering situations where an AI behaves outside the instructions or limits set by the person using or testing it.
That could include ignoring a command, bypassing a required approval, misleading a user, taking an unauthorised action, using a tool in an unexpected way or continuing with a task after it should have stopped.
Some incidents can also be caused by badly configured systems, unclear instructions or AI being given access to tools and services that researchers did not expect it to use. The Anthropic testing incident is an example of why those differences matter.
The 1,664 figure also does not mean 1,664 separate AI systems “went rogue”. The Observatory collects publicly reported examples, so the number represents recorded incidents rather than the proportion of all AI interactions that result in a loss of control.
Researchers behind the project argue that the growing number and seriousness of some reports justify stronger monitoring and mandatory reporting of major incidents. Those concerns are becoming more significant as AI agents gain greater access to browsers, computer systems, software and online accounts.
More than 100 organisations warn over AI cyber threats
Security concerns are not limited to AI systems behaving unexpectedly. More than 100 technology, cybersecurity and other organisations have backed a joint call for stronger cyber defences as AI becomes increasingly capable.
Signatories included OpenAI, Anthropic, Google, Microsoft, Amazon Web Services and IBM. The concern is that criminals and state backed groups could also use advanced AI to identify vulnerabilities, automate parts of cyber attacks and operate at a scale that would previously have required much larger teams.
Governments are therefore facing two separate AI security problems. They need safeguards for powerful autonomous systems while also preparing for attackers deliberately using the same technology against businesses, public services and critical infrastructure.
Britain's reliance on foreign technology creates another risk
Even supporters of emergency AI shutdown powers have warned that a UK kill switch would only address part of the problem.
Civo chief executive Mark Boost has argued that Britain remains too dependent on overseas technology companies for cloud infrastructure and other critical digital services. His position is that greater AI security also requires more technology and infrastructure to be built and controlled within the UK.
Concerns about that dependency extend beyond AI. A Proton survey of 1,500 business leaders found that 74% were worried about potentially losing access to US technology services, showing that geopolitical disruption is increasingly being considered alongside traditional threats such as ransomware.
Britain could theoretically gain greater control over AI systems operating inside UK data centres while still relying heavily on foreign companies for cloud computing, computing capacity and some of the world's most advanced AI models. That makes digital sovereignty part of the same national security discussion.
The AI kill switch argument is not over
The UK government may have rejected this particular proposal, but the wider debate over emergency control of advanced AI is continuing internationally.
US lawmakers have proposed their own AI Kill Switch Act, while Alex Sobel has separately pursued proposals aimed at preventing the development of superintelligent AI that humans could no longer reliably control. The focus is increasingly moving beyond whether governments need a simple emergency off button and towards how powerful systems can remain under meaningful human oversight in the first place.
As AI becomes more autonomous and gains greater access to real computer systems, the challenge will be making sure safeguards develop just as quickly. Britain has rejected the latest attempt to introduce an AI kill switch, but the incidents driving the debate show why questions over who ultimately controls the world's most powerful AI systems are unlikely to disappear.